

“Suddenly asked to verify my identity because of suspicious activity when logging in” — one of the most common messages Facebook users see. It doesn’t necessarily mean something is wrong with your account; more often the login environment triggered a security mechanism. This article gives you an actionable checklist: determine whether it’s possibly IP-related, then check and rule out each item. The discussion covers the role of IP in the network environment only; it does not describe platform-specific risk-control rules.
1. First, Understand What the “Suspicious Activity” Message Means
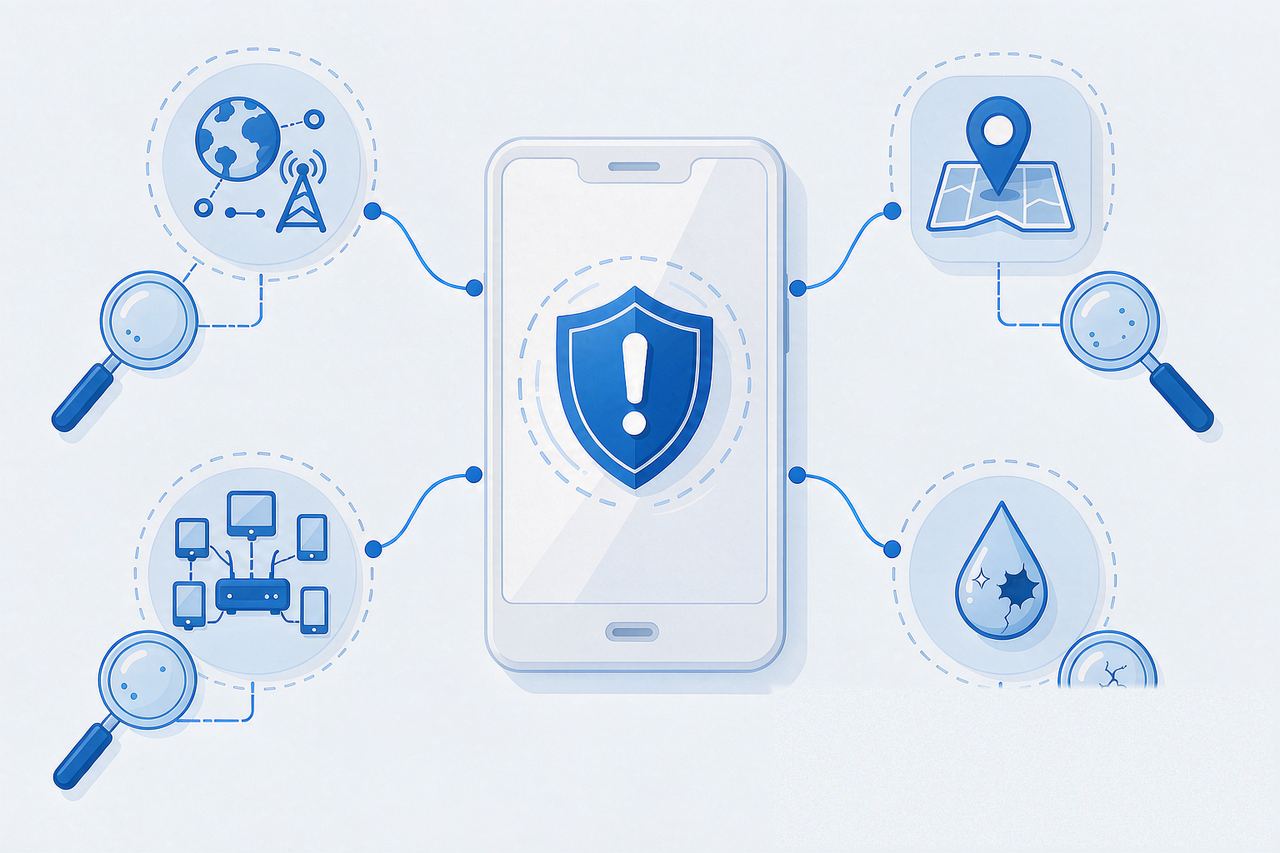
Facebook may trigger additional verification (CAPTCHA, identity confirmation) based on login environment, account activity, and other security signals. Potentially relevant factors include:
- Login region changes: the account usually logs in from region A, and recently from region B
- Network environment changes: exit IP type clearly differs from account history (e.g., long-time ordinary ISP network, recently Hosting/Data Center network)
- Multiple accounts sharing a network: several accounts using the same exit IP long-term, sharing some network environment signals
- Device/browser environment changes: device fingerprint or browser environment clearly inconsistent with history
Key insight: a prompt ≠ account banned. Such prompts usually mean the platform requests additional security verification; this article helps you check whether IP is a potentially relevant factor, so the problem doesn’t keep recurring.
2. IP-Dimension Checklist (In Order)
Item 1: Is the exit IP region consistent with account habits?
Use an IP detection page to confirm the current exit region. If the account has long logged in from country A and now logs in from country B (especially rapid cross-region jumps), this may form a larger environment change.
Item 2: Is the exit IP type consistent with history?
If an account has long used one type of network environment and suddenly switches to a clearly different type — for example, from an ordinary ISP network to a Hosting/Data Center network — this may form a larger environment change. For a self-check method, see Native IP vs Datacenter IP.
Item 3: Are multiple accounts sharing one IP?
Several accounts using the same exit IP long-term share some network environment signals; if other abnormal activity also exists, it may increase the likelihood of security verification. Prefer independent exit IPs across accounts.
Item 4: Is the environment leaking?
If DNS or WebRTC detection shows address information inconsistent with the current proxy exit, the browser environment may be exposing additional network information and needs further review. For troubleshooting, see the DNS/WebRTC leak fix guide.
3. After the Checklist: What to Do
If it may be IP-related:
- Align the region: log in with an IP region consistent with account habits
- Fix the environment: one account maps to one stable exit IP; avoid frequent switching
- Isolate accounts: different accounts use different IPs; reduce network sharing
If the prompt already appeared:
- Follow Facebook’s provided verification flow (the official channel)
- After verification, continue in a stable, expected network environment; avoid repeatedly triggering from the same problematic environment
No promises, but this is clear: handling IP-related network signals properly is one way to investigate and reduce recurring “suspicious activity” prompts; whether the platform triggers verification still depends on the overall account and network assessment.
4. FAQ
Q: Does “suspicious activity” mean my account is restricted?
A: Such prompts usually mean the platform requests additional security verification, and do not equal a permanent restriction. Whether normal use resumes depends on the platform’s actual prompts and account status.
Q: Will changing IP prevent “suspicious activity” prompts?
A: Simply changing IP doesn’t guarantee avoiding the prompt. If the issue is indeed related to network environment changes, keeping a stable, reasonable network environment consistent with the account’s normal usage may help reduce repeated verification; whether the platform triggers verification still depends on other factors.
Q: What should I watch after verification?
A: Keep the network environment relatively stable (same region, same exit IP type, no obvious leaks); avoid large short-term jumps across regions or network types.
5. Summary
The “suspicious activity” checklist: check region consistency → check IP type consistency → check shared networks → check leaks. Running through these four items helps determine whether the issue may be related to IP and the network environment. Principles: align, fix, isolate, don’t leak. Handling the network environment properly reduces the chance of these prompts recurring.
For ad-account protection ideas, see Facebook Ads Account: IP-Focused Protection. If you need a long-term stable, fixed-exit network environment, IPNut‘s Static Residential ISP offers fixed IPs by region — it’s a network environment choice; whether platform verification triggers remains subject to the platform’s actual assessment.